
Announcement
Check out new writeups!
224 words
1 minute
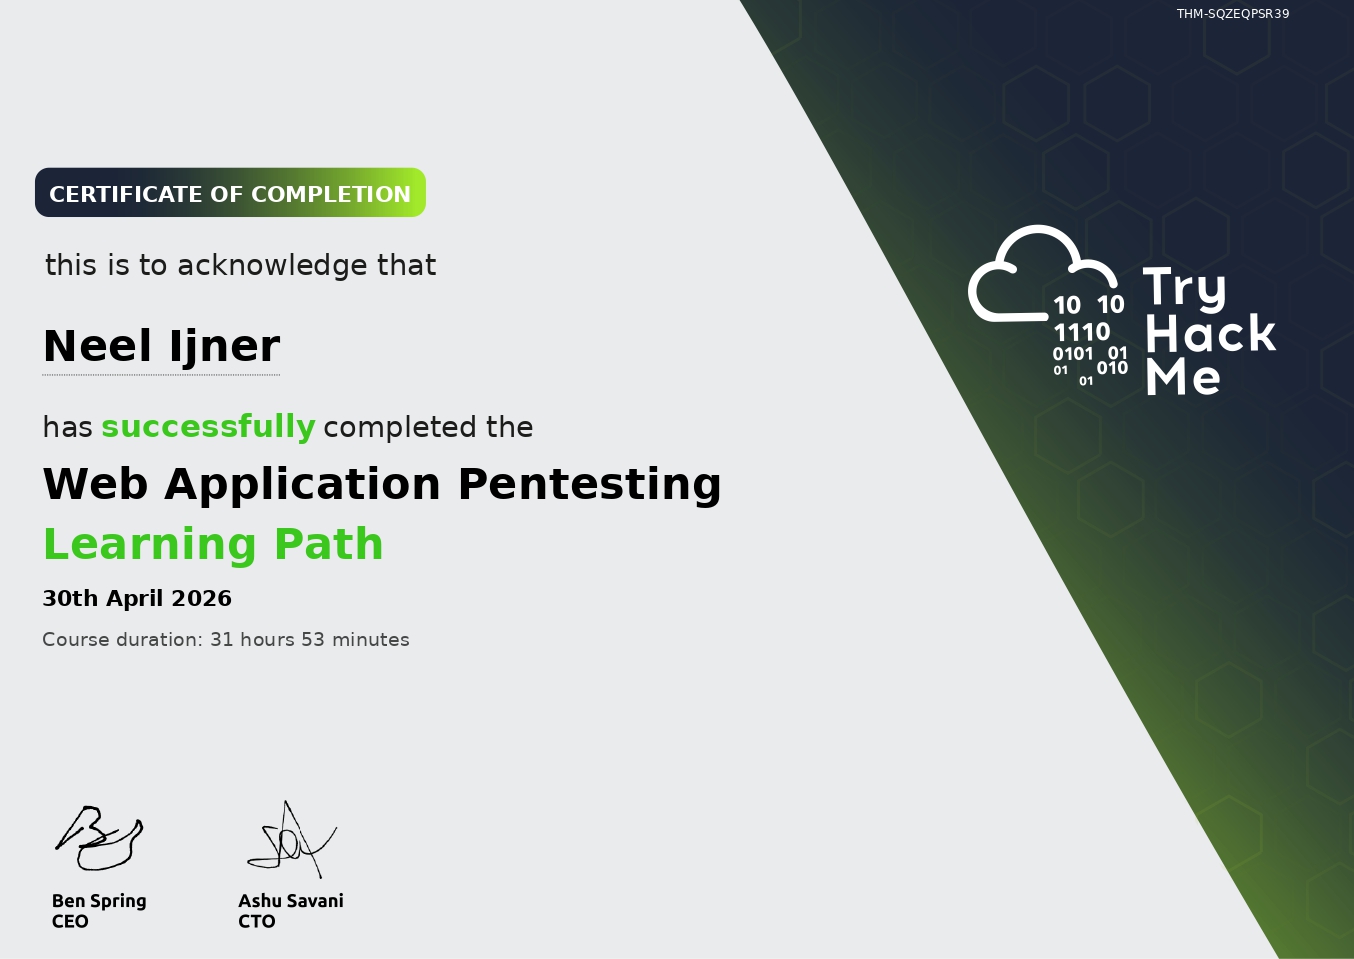
TryHackMe Web Application Pentesting Path - Completed
Just finished the Web Application Pentesting learning path on TryHackMe. This one was significantly harder and way more programming-heavy than the previous paths. Honestly, a good thing to learn deep enough to actually exploit websites properly.
Modules Covered
- Authentication Attacks - Learned about auth security testing and lots of ways to attack and bypass authentication systems
- Injection Attacks - Advanced injection attacks, not just basic stuff but advanced techniques with much deeper knowledge
- Advanced Server-Side Attacks - Same as above, advanced stuff with new modern techniques for pentesting
- Advanced Client-Side Attacks - Advanced client-side attacks: XSS, CSRF, DOM, CORS, etc.
- HTTP Request Smuggling - The most brain-eating stuff. HTTP Request Smuggling can access internal resources, bypass permissions, cause privilege escalation, and even RCE
End of Learning Phase
This marks the end of the learning phase for now. I spent 1.5 months after my internship, learning advanced methods and techniques to pentest and hunt for bugs in websites. Also learned red teaming stuff and lots of CTF-related tools and methods.
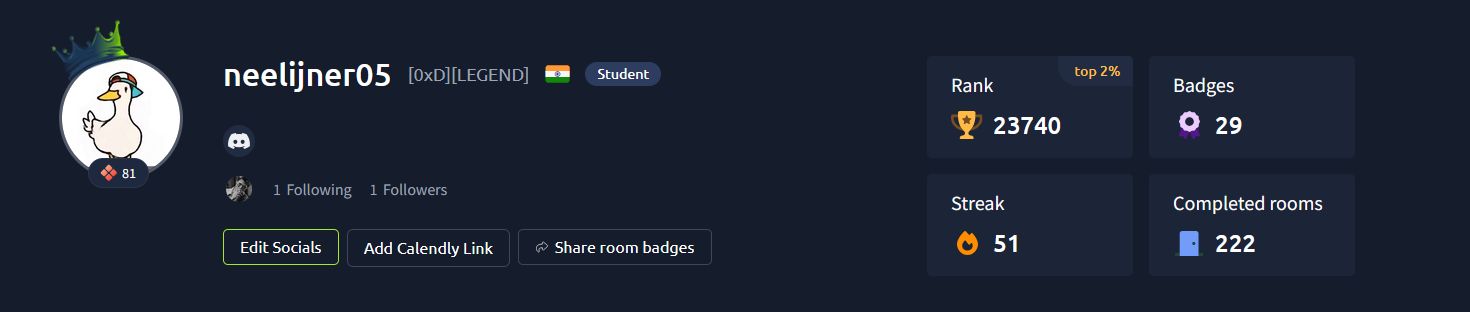
Now I’ll focus on actually using this learning on CTFs and Bug Bounty. Btw, I reached top 2% on TryHackMe with a 50-day streak, which is massive for me. Consistency is a very hard skill to master.
Happy hacking!