
I just wrapped up two major learning paths on TryHackMe: Jr Penetration Tester and Web Fundamentals. Honestly, the experience was amazing, mainly because it was full-on hands-on practical work. If you’re tired of dry theory and just want to get your hands dirty with actual machines and vulnerabilities, these paths are exactly what you need.
Just like my experience with the SEC1 exam, these paths skip the fluff and dive straight into the “how-to”. It’s one thing to read about an attack, but it’s a whole different feeling when you actually execute it on a target machine.
What I Learned (The Practical Way)
Instead of just sitting through slides, I spent my time actually doing things. Here’s a quick look at the core stuff I tackled:
- Privilege Escalation: I spent a good amount of time learning how to go from a low-level user to root/admin on both Linux and Windows systems. It’s all about finding those misconfigurations that shouldn’t be there.
- Shells & Reverse Shells: Mastered the art of getting that initial foothold and then upgrading it to a more stable shell.
- Burp Suite Mastery: Probably one of the most useful tools I’ve learned. From intercepting traffic to automating attacks, Burp Suite is a beast for web testing.
- Nmap & Metasploit: Spent a lot of time on Nmap mastery for network discovery and Metasploit for exploiting known vulnerabilities.
- Web Attacks & OWASP: Dove deep into the TOP OWASP attacks like SQLi, XSS, and IDOR. It’s eye-opening to see how common these still are.
- API Testing: Learned how to poke around APIs and find security holes in how data is being handled.
- Methodology & Enumeration: This was a big one. Learning a solid penetration methodology and the importance of thorough enumeration changed how I approach any target. If you don’t enumerate properly, you’re just shooting in the dark.
Final Thoughts
The best part about these paths is that they are fully practical. There’s almost zero “just read this” sections—it’s all about “do this and find the flag.” It was incredibly helpful in bridging the gap between knowing a concept and actually being able to use it in a real-world scenario.
If you’re looking to build actual skills that you can use, I can’t recommend these enough. It’s been a great journey so far, and I’m definitely looking forward to the next challenge!
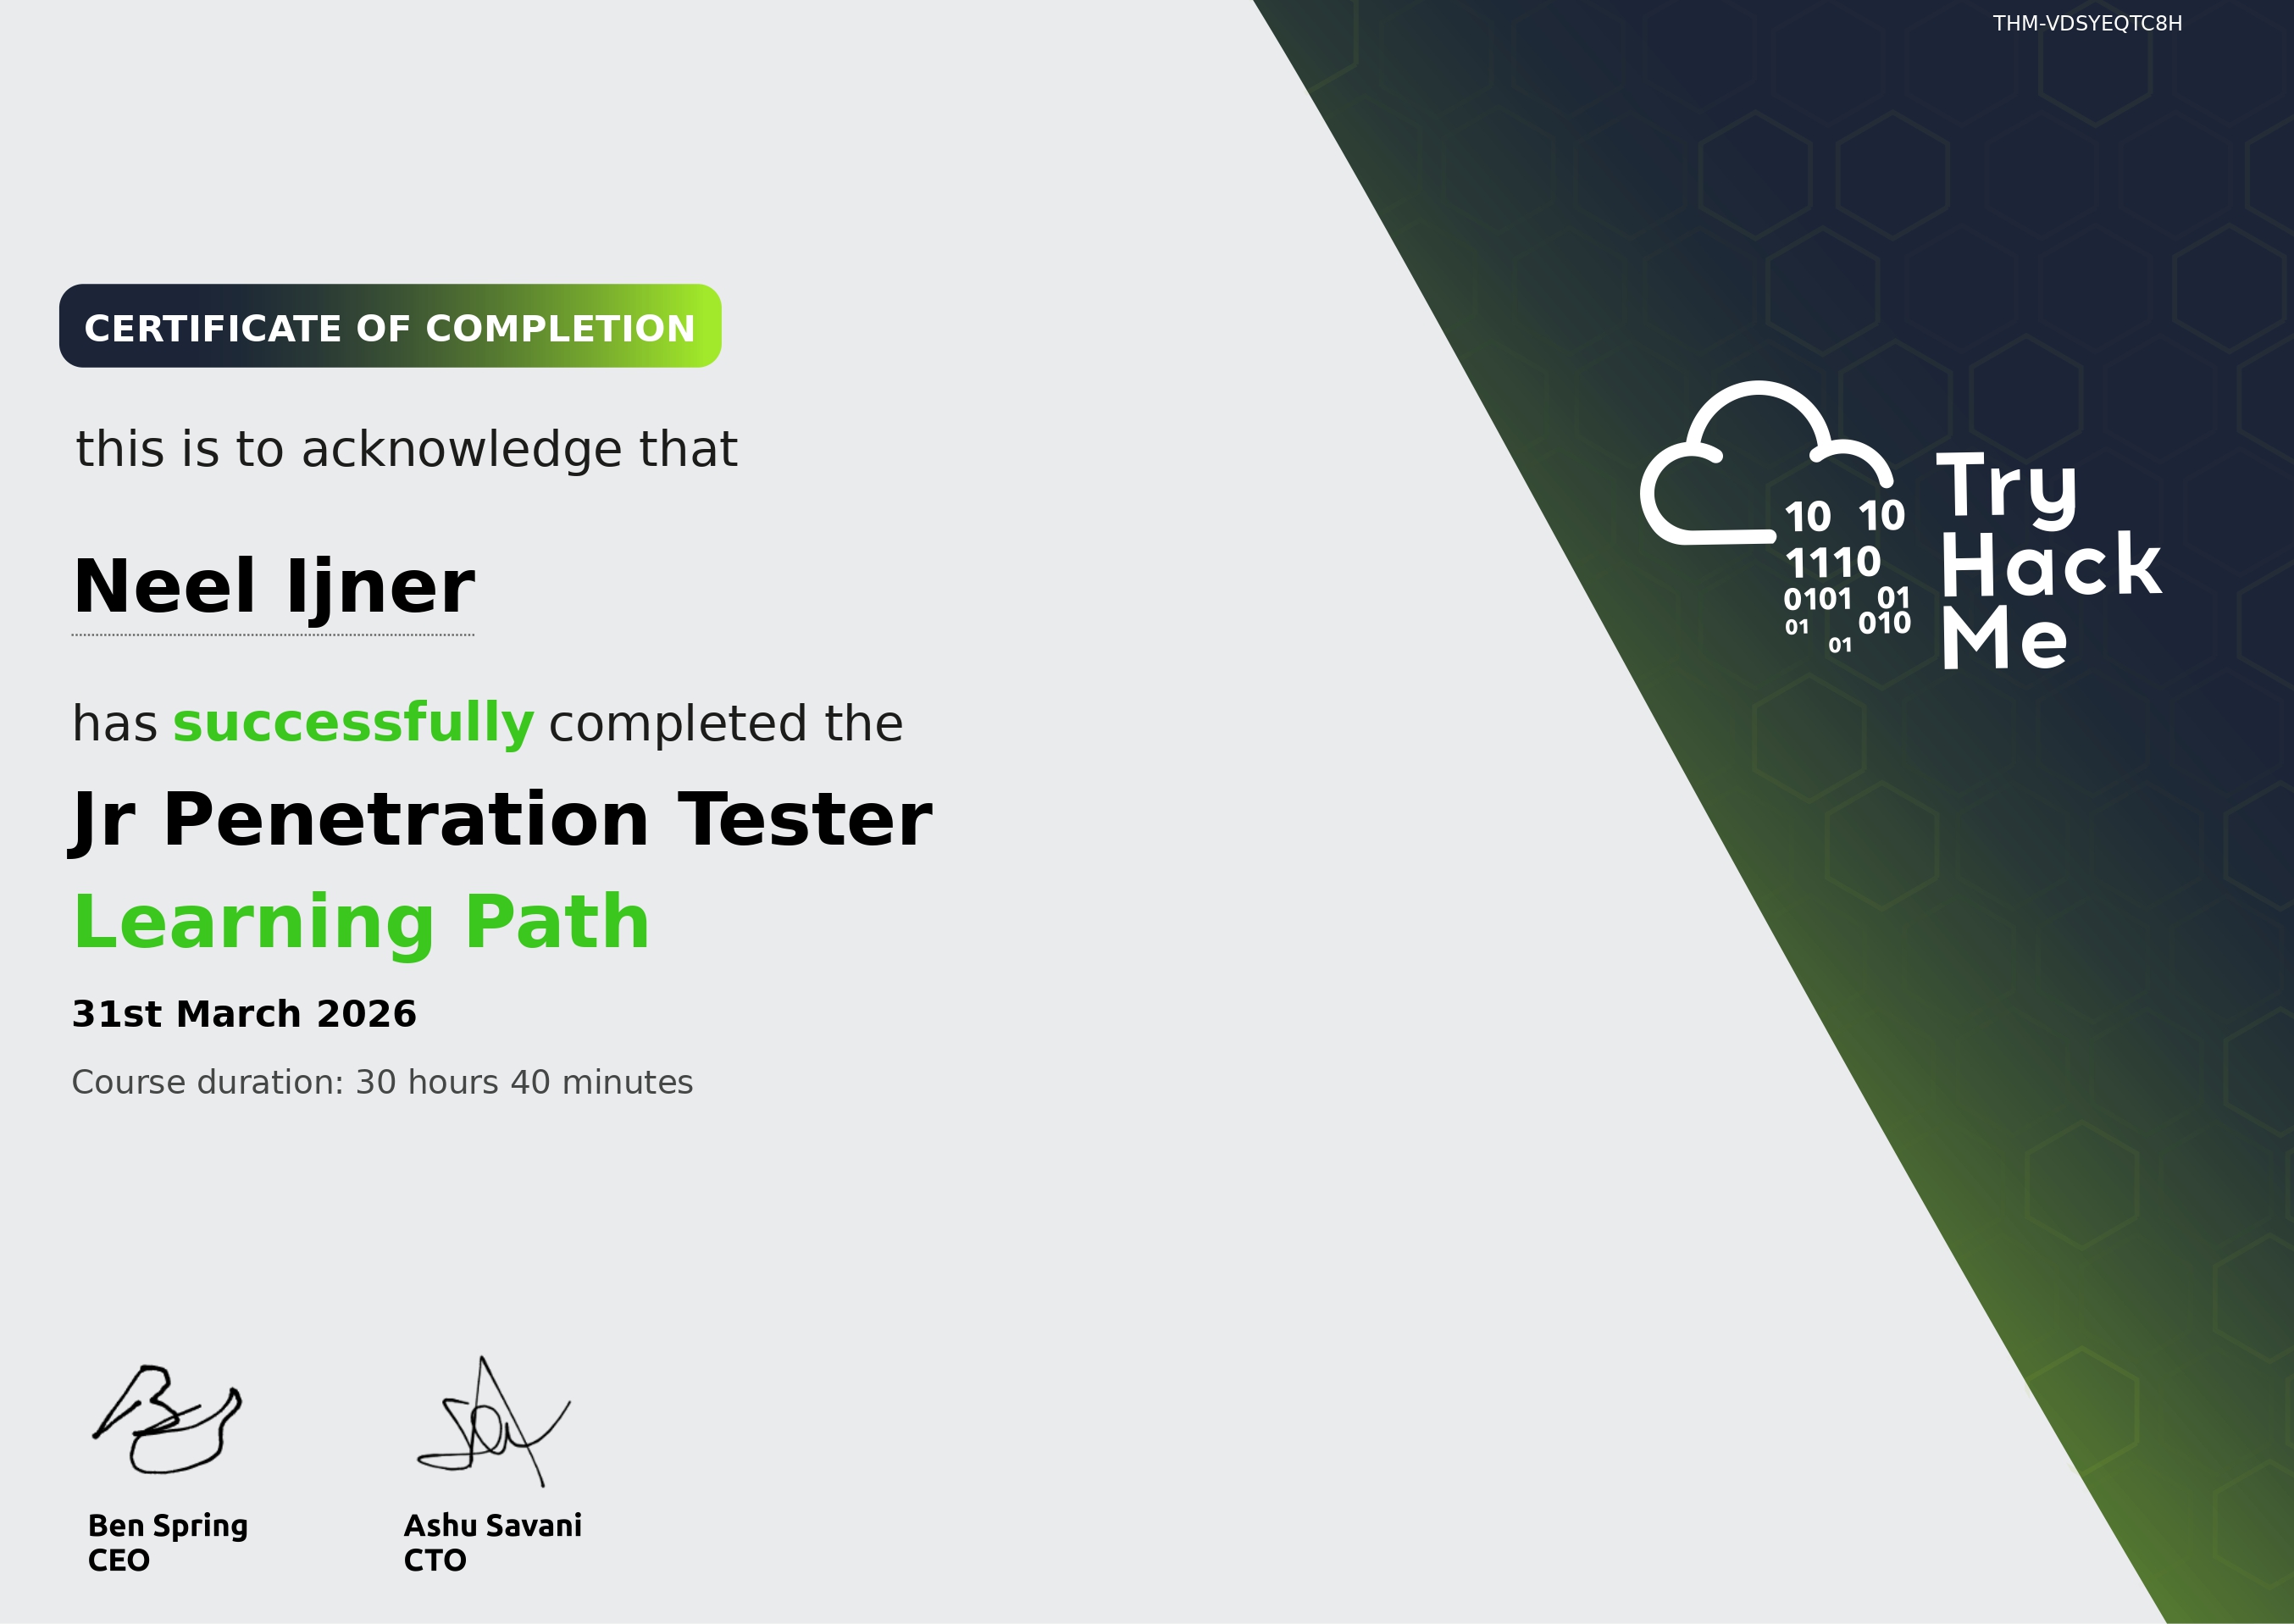
Here are the certificates for completing the paths:

Happy hacking!
Some information may be outdated