
I just finished the New AI Security Path on TryHackMe. Honestly, it was a win-win situation: I got to dive into the world of AI security and, since there’s a raffle giveaway, I might even snag some swag or a premium subscription. Win-win, right? Hehe.
This path was broken down into five core modules that really pushed my understanding of how AI works and, more importantly, how it breaks.
Breaking Down the Modules
- AI Fundamentals: This was all about the basics LLMs, models, and the common threats facing them. I even learn little bit of AI Forensics.
- Securing AI Systems: I learned how vulnerable these systems actually are. This module focused on the specific attack surfaces that threat actors target when messing with AI.
- Prompt Injection: This was the highlight for me. I got to practice actual attacks like jailbreaking and system prompt reveals. It wasn’t just about attacking, though; I also learned the defensive side of how to stop these injections.
- AI Supply Chain Security & Data Poisoning: These last two modules were definitely the hardest to wrap my head around. I explored RAG (Retrieval-Augmented Generation), its specific attack vectors, and how the AI supply chain can be compromised.
Final Thoughts
I’ll be honest—this path felt a bit more Blue Team heavy than I expected, with less focus on pure Red Team attacks. I haven’t fully digested every single detail yet, especially the supply chain stuff, but it has given me a solid foundation-to-mid-level understanding of the field.
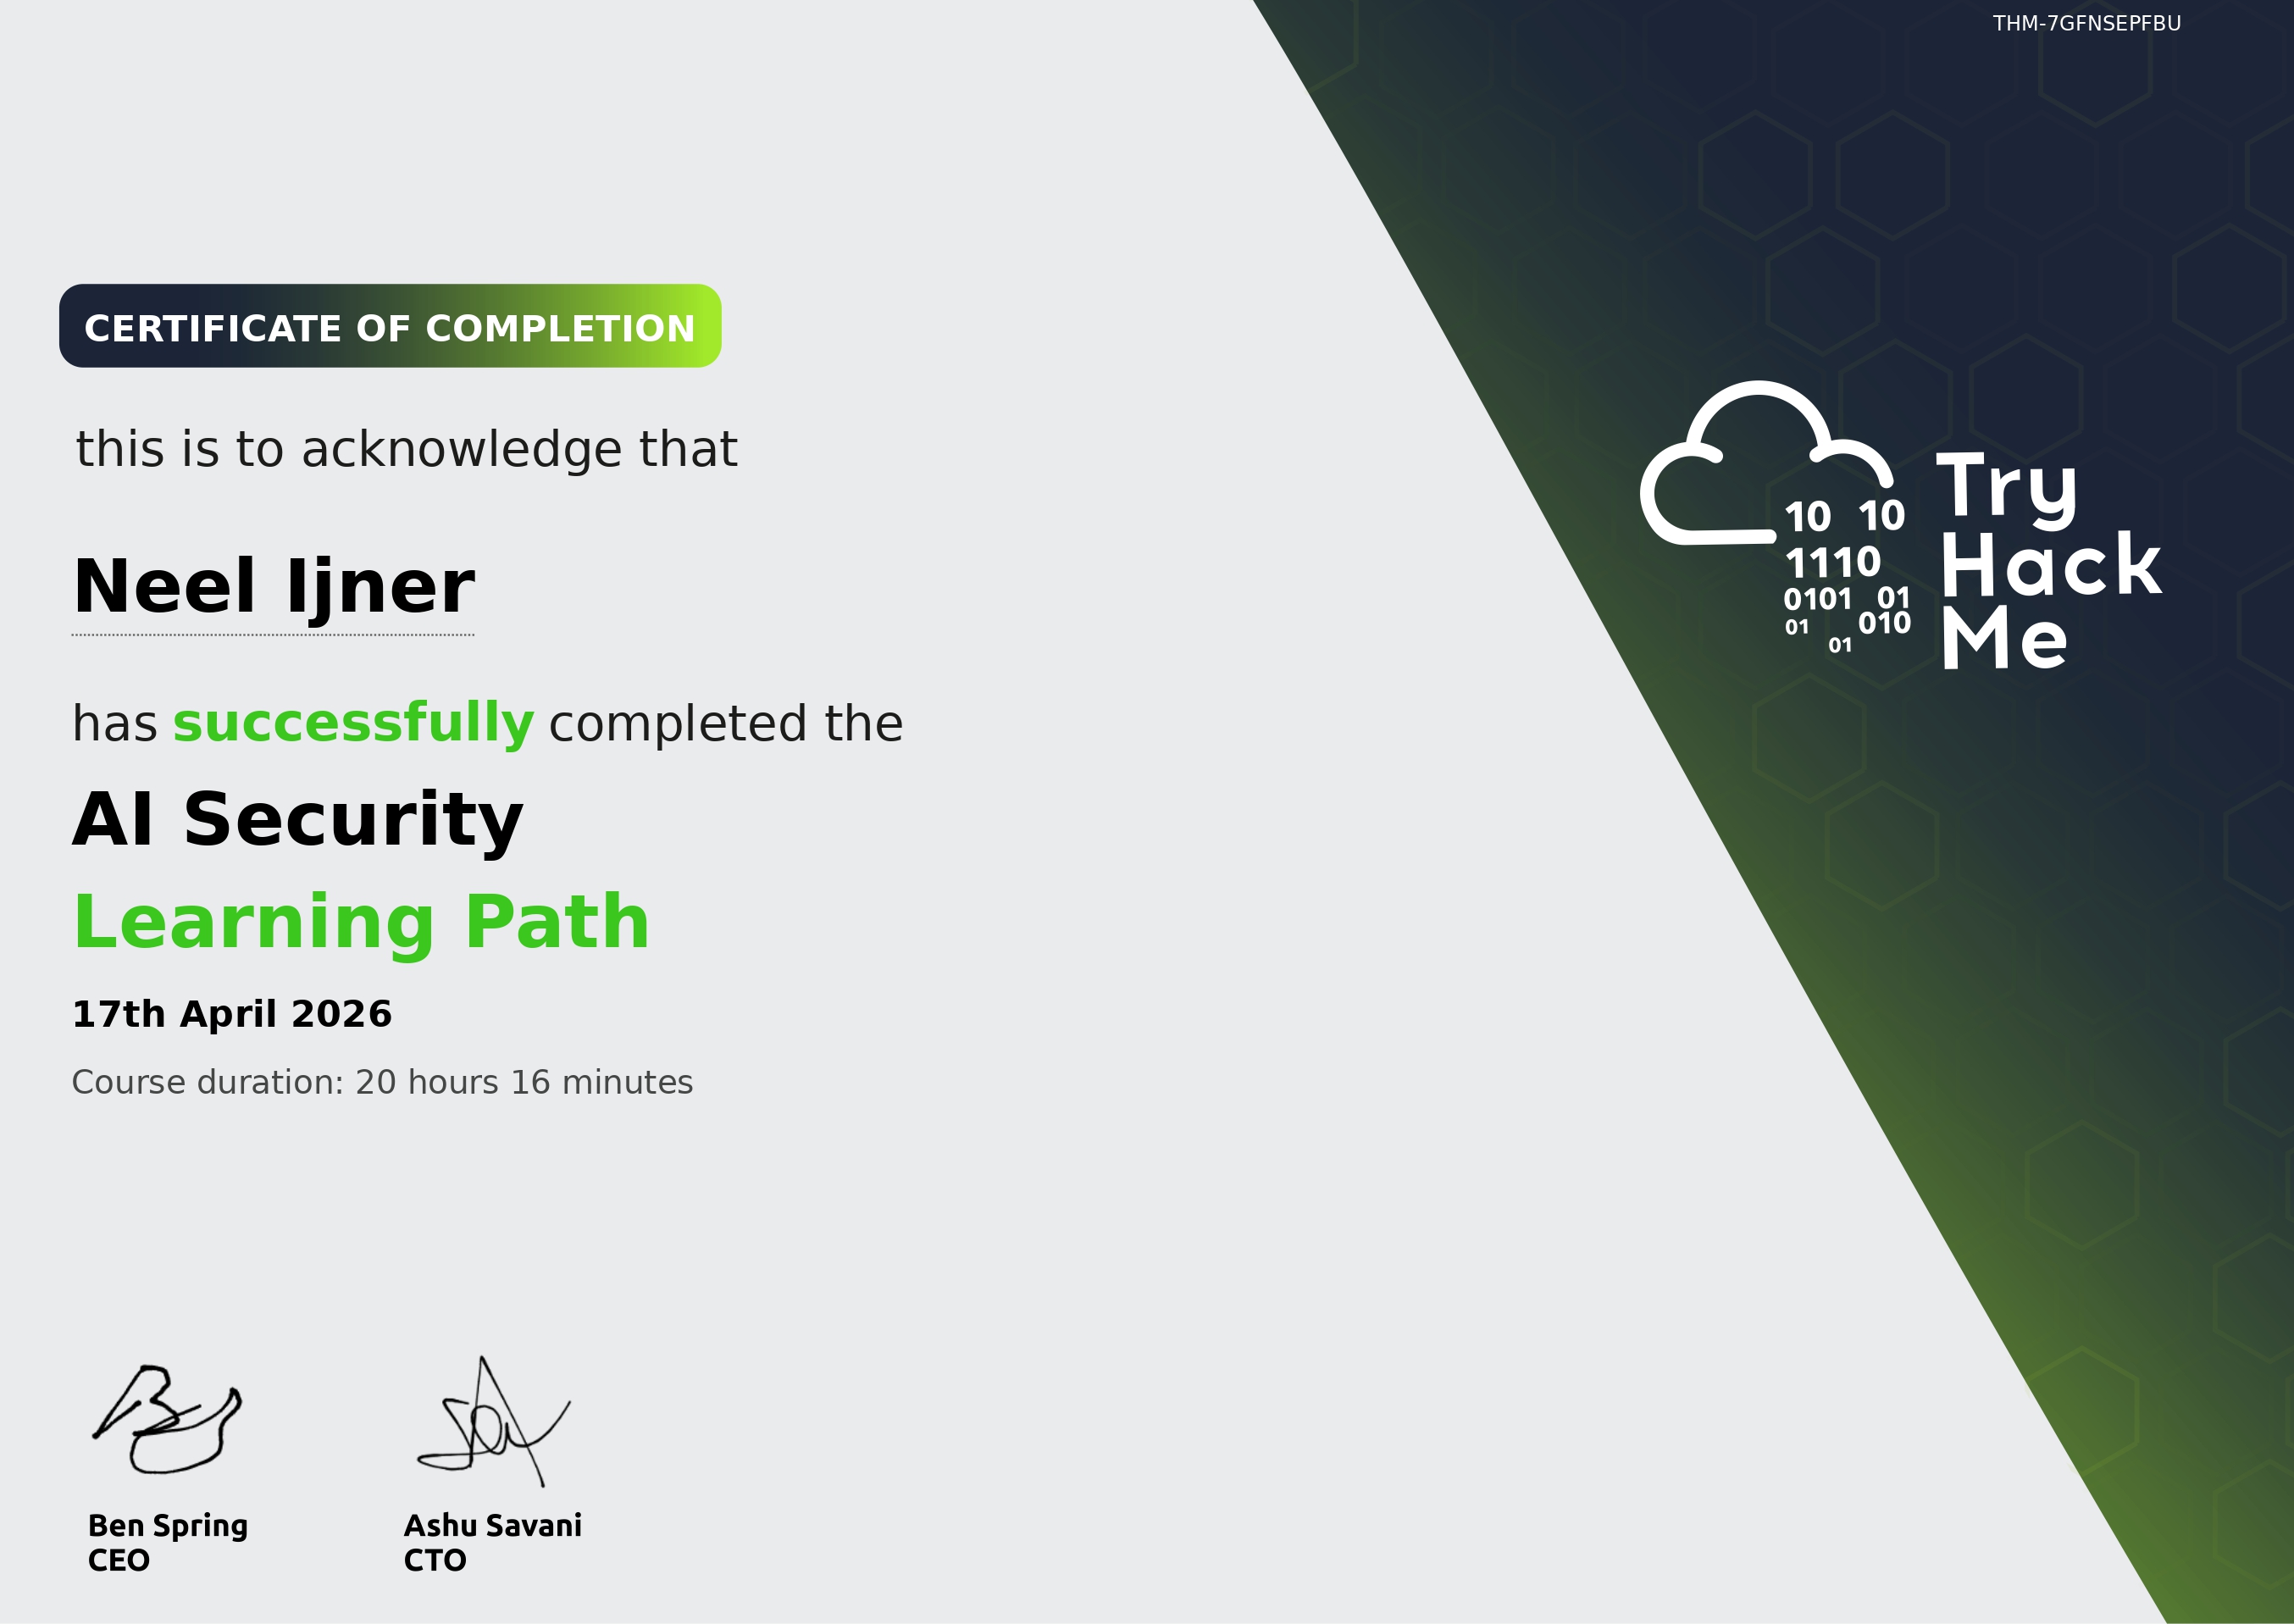
It’s a great starting point for anyone looking to see where the industry is heading. I still have a lot to learn, but I’m glad I’ve built this foundation. Now, let’s hope I win that raffle!
Happy hacking!